Narrated by Study Buddy Narration
Voiceover Engine • Interactive Audio Sync
0:0010:00
Learning Objectives & Key Takeaways
0 / 4 Completed- Understand Kubernetes & Docker core architecture and runtime execution model
- Audit real-world latency, throughput benchmarks, and memory footprint
- Implement zero-downtime deployment patterns with resilience guards
- Verify code snippets and architect blueprints against production SLOs
🚀 Architecture Ready
100%
What you will learn
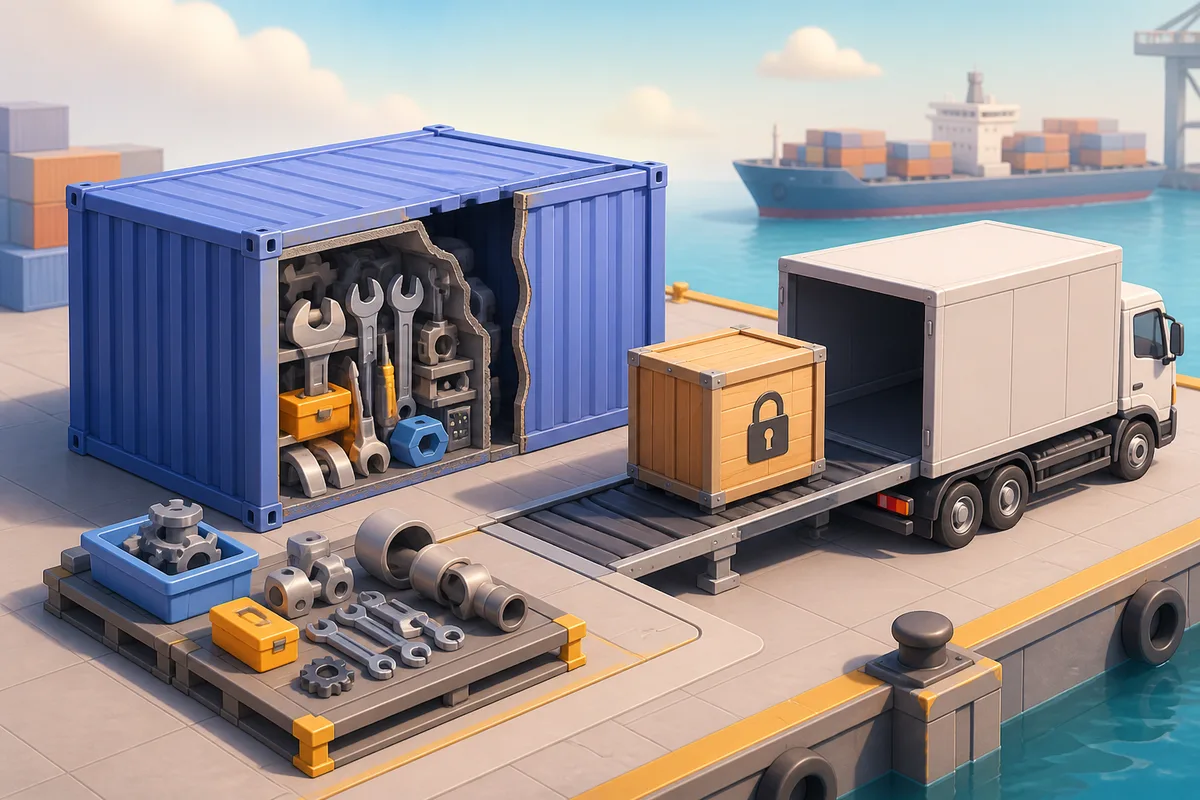
- Multi-stage builds separate compilers and package managers from the artifact that actually ships to production.
- Distroless or scratch final stages remove shells and package managers, shrinking attack surface, not just image size.
- COPY --from=<stage> only transfers what you explicitly name, so runtime dependencies must be copied deliberately.
- Kubernetes securityContext settings like readOnlyRootFilesystem and dropped capabilities complete what the image alone cannot enforce.
- A smaller image is not an unscanned image; Docker Scout and CI-based validation remain mandatory.
The Pager Went Off Because of a Shell Nobody Used
Our security team ran a routine scan against the production image for our internal billing API and flagged forty-one CVEs, several rated critical, all living inside a shell and a package manager that no running process ever touched.
The image was built with a single FROM node:18 statement, copied the entire repository including devDependencies, test fixtures, and a stray .env.example file, and weighed in at 1.2 gigabytes.
In the rest of this story
- Why Multi-Stage Builds Exist
- Rebuilding the Billing API the Right Way
- When Scratch Beats Even Distroless
- The Image Is Only Half the Job
- Scanning and Signing Are Not Optional Extras
Member-only story
Checking your membership…
Members read every Tech Buzz story in full, with code examples, audio and the discussion, plus every course, quiz and interview set in the Learning Dashboard.
Previous Story
The HR Chatbot That Almost Leaked Salary Bands: Lessons from Bedrock Guardrails
 AWS & DevOps•10 min read
Next Story
3 AM Page: Our URL Shortener's Database Melted Under a Billion Redirects
 System Design•10 min read

Written By
MCB Editorial
Tech Buzz Daily Desk. Contributing deep-dive engineering architectures, cloud paradigms, and system design insights to Master Class Buddy.